Tokyo police urge 14 franchise companies to strengthen cyber security and review personal data management
Tokyo’s Metropolitan Police Department held a cyber security seminar for franchise businesses and other companies on 28 October, urging 14 association members to delete personal data past its retention period and manage their systems properly.
Published
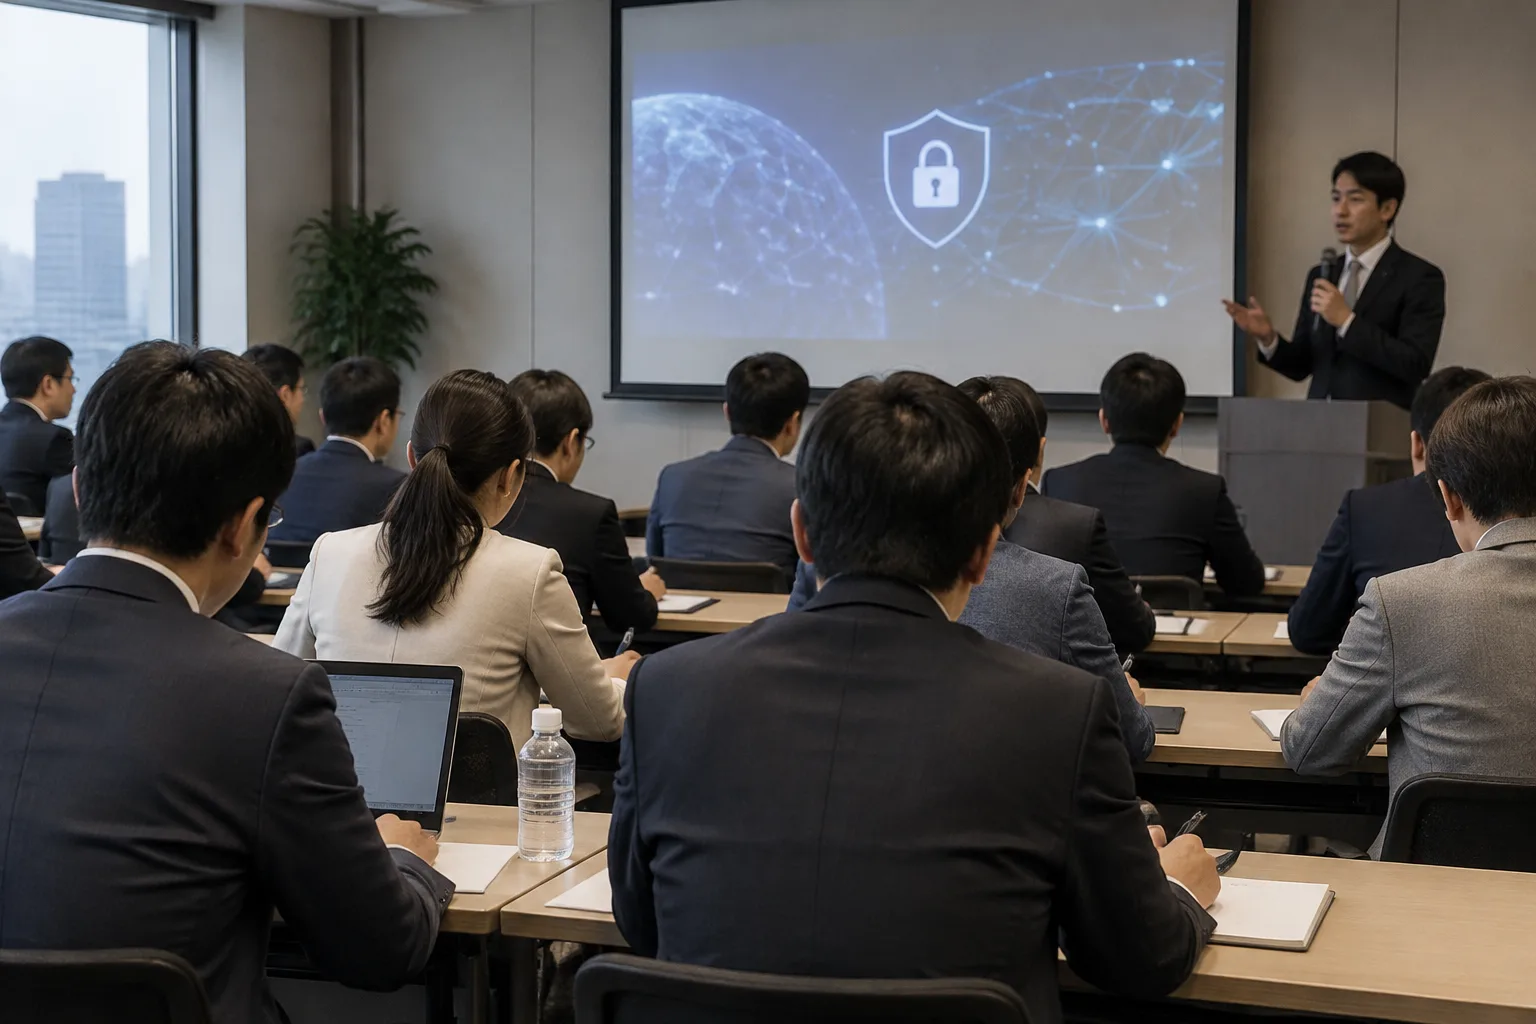
Tokyo’s Metropolitan Police Department held a cyber security seminar in the capital on 28 October 2026 for companies including those operating franchised restaurant chains. According to Jiji Press, 14 member companies of the Japan Franchise Association attended. Amid a series of personal data breaches, police urged businesses of all sizes to take preventive action.
Businesses of any size could be targeted
A police representative at the seminar warned that businesses “could be targeted regardless of their sector or size”. The message was that cyber security is not just an issue for large companies: every business needs to review its day-to-day information management.
The seminar’s audience included companies operating restaurants through a franchise model. The figure of 14 refers to participating association member companies, not the number of outlets represented. Nor was this an announcement that those 14 companies had suffered data breaches; the event was held to encourage preparedness for cyber attacks.
For the franchise community, the key point is not to underestimate risk on the basis of company size. When franchisors and franchisees assess their preparedness, the practical starting point should be to establish what information they handle and how they manage it, rather than assume that their business is unlikely to be targeted.
Watch for unaddressed vulnerabilities and infections at service providers
The police representative explained the capabilities and characteristics of artificial intelligence (AI) believed to be used in cyber attacks. The discussion went beyond AI, warning that unaddressed system vulnerabilities and malware infections at outsourced service providers could also lead to data breaches.
This highlighted two areas to review: a company’s own systems and its external service providers. Alongside managing internal systems, businesses need to examine outsourced operations. Outsourcing a task should not, in itself, be treated as the end of a business’s checks on information management.
Franchisors and franchisees looking to act on the warning could begin by compiling an overview of the systems they use and the work they outsource. Identifying the people responsible for managing these arrangements, along with relevant contact points, would then make it clearer who to approach if a problem arises. This is a practical suggestion based on the warning, not an indication that the seminar established a new standard procedure.
Understanding the potential use of AI in attacks and managing existing systems should be considered together. Businesses need to stay informed about new technology while also reviewing basic controls, including whether known vulnerabilities have been left unresolved.
Delete personal data once its retention period has expired
The specific measures requested by the Metropolitan Police Department were the deletion of personal data past its retention period and proper system management. The request therefore covered not only the safeguards used to protect information, but also a review of the information being held.
Importantly, this was not a call to delete all personal data indiscriminately. It concerned data whose retention period had expired. In practice, businesses should first establish which retention period applies to each category of information, then identify and remove data held beyond that period. They should also check whether actual storage practices match their retention rules.
Where both a franchisor and its franchisees handle information, clarifying the scope of each party’s responsibility is a useful first step. For example, establishing who checks retention periods and who carries out deletion can help prevent tasks from being left unfinished because responsibilities are unclear.
Businesses considering their response should begin by assessing their current arrangements. Separately reviewing expired data, system management and questions for service providers can help turn the warning into concrete checks.
An opportunity for franchisors and franchisees to agree what needs checking
The seminar was an initiative by the Metropolitan Police Department to call directly on franchise businesses and other companies to take action. Its central themes were vigilance against attacks, an understanding of how breaches can begin, and the management of personal data and systems.
When sharing this information across a franchise network, it is worth going beyond passing on the warning to identify what needs checking within each business’s operating structure. Distinguishing between matters managed by the franchisor, those managed by franchisees and those requiring confirmation from external providers is a useful starting point.
Practical takeaway: Use this warning as an opportunity for franchisors and franchisees to check three things together: whether any personal data remains beyond its retention period, whether responsibility for system management is clear, and whether the questions that need to be put to service providers have been identified.