Refrigeration systems hacked in Sicily: the franchising implications
Three Arena franchisees and Radenza-operated Coop stores were among those affected. For franchise networks, equipment security and operational responsibilities are now key concerns.
Published
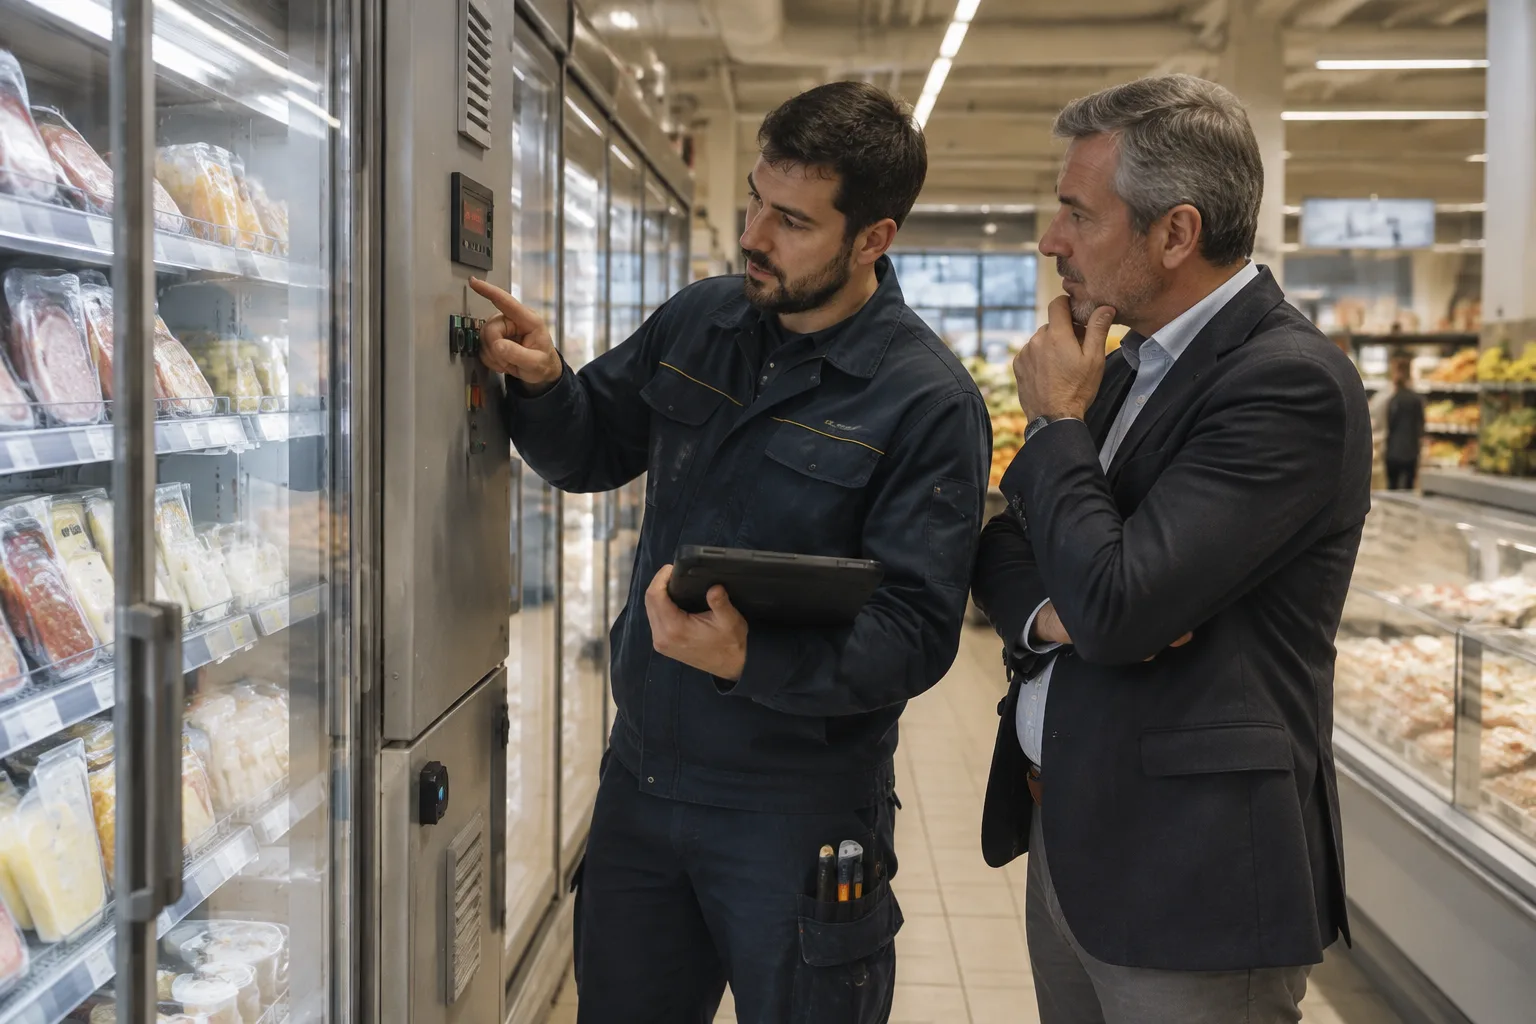
Cyberattacks can also compromise the cold chain. Overnight on 1–2 November 2026, the remote management systems controlling refrigerated display units at around 20 Sicilian supermarkets were tampered with remotely. Franchise stores were among those affected, bringing the relationship between head-office rules, equipment management and franchisees’ operational responsibilities into focus for the franchising sector.
The attack on refrigeration systems
According to a report published by L’Express Franchise Italia on 4 November, the attackers targeted systems used to control refrigeration equipment remotely. They activated defrost cycles and changed operating settings, breaking the cold chain.
In some cases, temperatures reached 50°C. Fresh and frozen products consequently had to be discarded. The reported damage therefore directly affected stock and equipment operation, rather than simply involving access to information or the availability of IT systems.
The supermarkets reported to have been affected include Coop stores, some Conad outlets and three franchisees of Gruppo Arena, which belongs to the VéGé retail group. Following the attacks, Italy’s National Cybersecurity Agency issued an alert to retailers.
The way the attack was carried out highlights a practical issue: when essential equipment can be controlled remotely, securing that access becomes part of a store’s business continuity arrangements. In Sicily, digital tampering had physical consequences for the products in storage.
Arena: three franchisees affected and rules not fully implemented
For Gruppo Arena, the reported impact was limited to three franchise stores out of a network of around 200 outlets. Chief executive Giovanni Arena, who is also the Sicily representative for retail trade body Federdistribuzione, said the three stores had not fully implemented the security rules set by head office.
This is an important point for franchisor–franchisee relations. Having central guidelines in place is not the same as ensuring they are applied in each store. The case underlines the need to consider both aspects when assessing the security of connected equipment.
The information reported does not establish specific contractual liabilities or identify which individual measures had not been implemented. It would therefore be inappropriate to treat the statement about incomplete compliance as a conclusion about who is financially liable for the damage.
For franchise networks, the practical question is instead how to check that agreed procedures are understood, applied and maintained over time, including where the franchise store is responsible for day-to-day equipment management.
Radenza: police report filed and stores remain operational
The affected Coop stores are operated by Radenza, Coop Alleanza 3.0’s master franchisee in Sicily, with around 300 outlets. Managing director Giuseppe Spadaro confirmed attacks on at least three stores in Catania and one in Palermo, beginning at around 4 am.
The group filed a report with Italy’s postal and communications police, which handles cybercrime, and notified the National Cybersecurity Agency. At the time of the published reports, the damage was still being assessed, so no figure was available for the losses incurred.
Radenza also reassured customers through its own channels, stating that stores remained open and operational. Continued trading and the financial assessment of the incident are separate matters: maintaining service does not mean there was no damage, which the group was still assessing.
Useful checks for franchisors and franchisees
For the franchising sector, the incident suggests that connected equipment should be among the issues examined within the franchise relationship. This is not about announcing new regulatory obligations or contractual changes already in place, but about identifying questions to address before an emergency occurs.
Who authorises remote access? Who decides on updates and pays for them? How is compliance with head-office procedures checked? And who should be notified when an abnormal temperature signals a possible malfunction or tampering?
These are organisational checks for the parties to agree on, without assuming that every contract allocates responsibilities and costs in the same way. The Sicilian case shows why cybersecurity deserves attention even in activities that appear far removed from data.
Practical guidance: franchisors and franchisees can start with a joint review of remote access, updates and emergency contacts for refrigeration equipment, setting out in writing who must respond and which procedures they should follow.