Call for Mandatory Cybersecurity Standards for Franchise Businesses
Comments published by Al-Masry Al-Youm call for franchise businesses to be required to protect customer data, but do not announce any new regulations.
Published
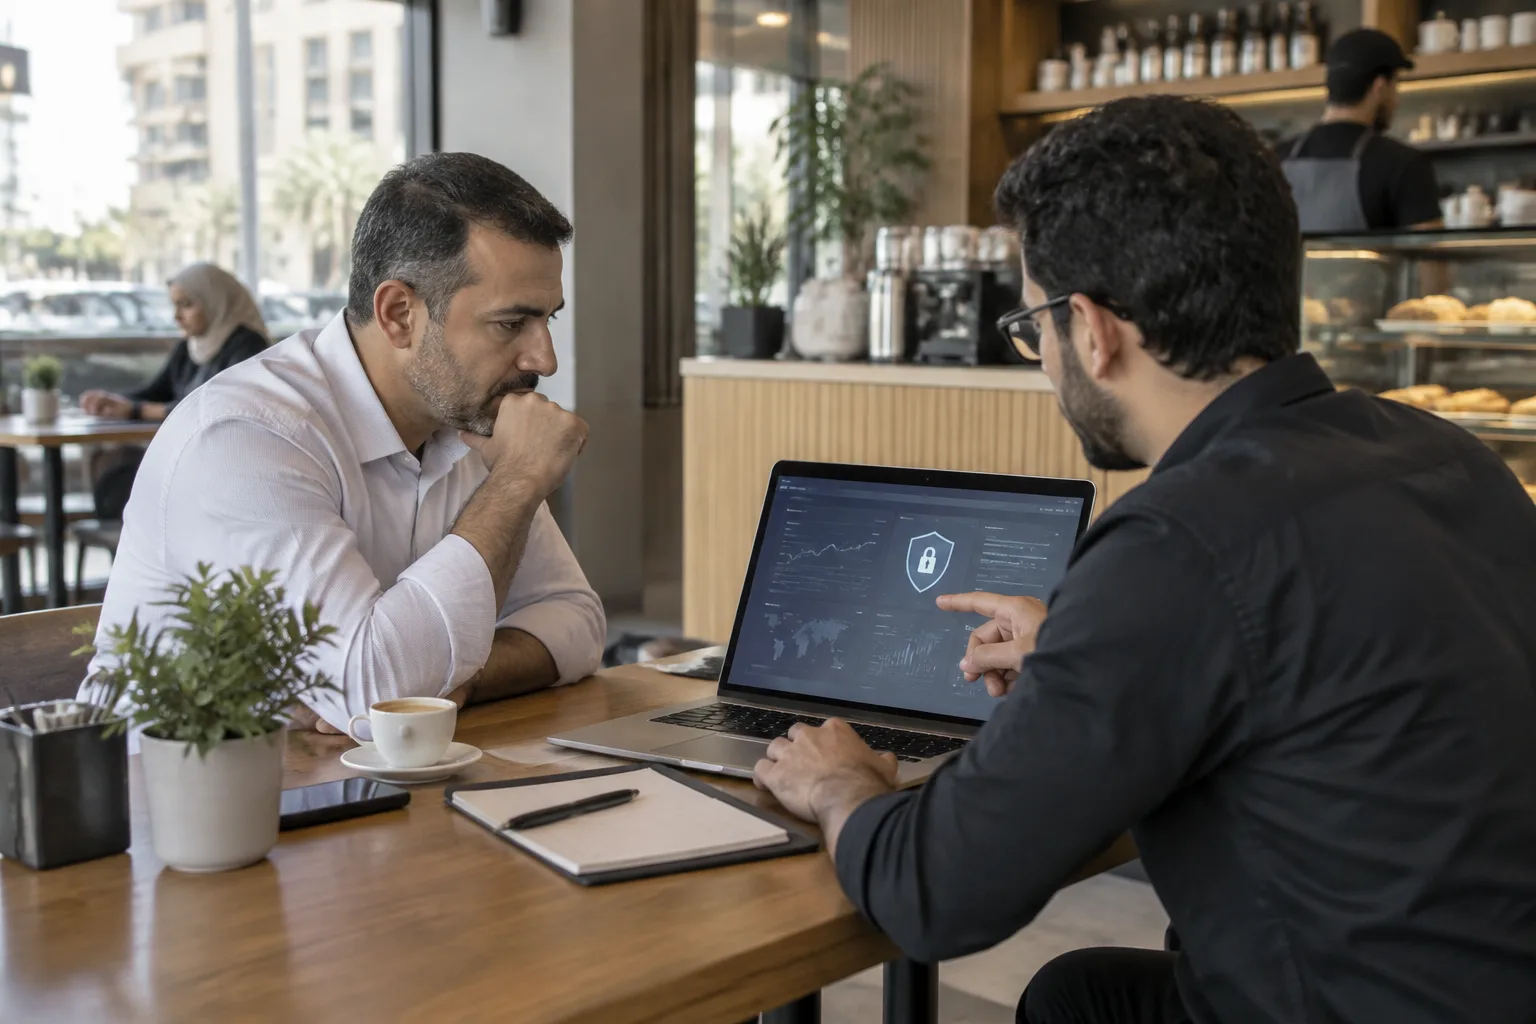
Customer data protection in the franchise sector came into focus in comments by a technology expert published in the Egyptian newspaper Al-Masry Al-Youm on 28 September 2026. The expert called for businesses to be required to meet cybersecurity standards. The comments raise the question of franchise businesses’ responsibility for the sensitive data they hold, but do not announce a new law or regulatory change in force in Egypt.
Data protection is not just a concern for large organisations
According to the published extract from the report, the expert stressed that the challenge is not confined to large organisations: franchise businesses also hold sensitive customer data and should be required to meet protection standards. The comments therefore place franchise businesses firmly within the debate on data security, rather than treating it as an issue solely for larger institutions.
For Egypt’s franchise sector, the significance lies in the focus on a business’s responsibility for the information it holds. The call is not based on the size of a brand or the number of its branches, but on whether it holds sensitive customer data that needs protecting. This was the basis for the expert’s demand that these businesses be required to meet security standards.
The extract does not name any businesses or report a breach at a franchise brand. The comments should therefore be read as a general call for businesses to take a stricter approach to data protection, not as a warning about a specific incident within Egypt’s franchise sector.
A call for mandatory rules, not an announcement of legislation
According to Al-Masry Al-Youm, the expert said: “Cybersecurity cannot be left to voluntary choice; it must be governed by strict laws.” This expresses support for moving from voluntary action to legal obligations, but does not in itself establish that legislation or a regulatory decision has been issued.
This distinction is essential for brand owners and investors in the franchise sector. The available report records an expert’s call for binding rules; it does not provide new legal provisions or a timetable for introducing additional requirements for franchise businesses in Egypt. Nor does the extract give details of proposed penalties or identify an authority that would enforce the measures advocated.
An accurate reading therefore requires a distinction between the direction of the debate and the regulatory position. The call should not be turned into a headline suggesting that mandatory audits have begun or that cybersecurity-related licensing requirements have been introduced. At the same time, the comments offer businesses an opportunity to discuss how clearly their data protection responsibilities are defined, without making assumptions about decisions the source has not announced.
The Saudi experience in context
The expert cited Saudi Arabia’s experience as an important example, saying that businesses there undergo periodic reviews to ensure data protection. This reference supported the argument for mandatory requirements and oversight; it was not an announcement that a particular regulatory model would be adopted in Egypt.
The available extract does not name the Saudi authorities involved, specify which businesses are covered or state how often those reviews take place. The comparison therefore remains an account attributed to the expert by the newspaper. On its own, it does not provide a basis for a detailed description of the Saudi system or for inferring legal obligations on Egyptian businesses.
For the franchise sector, the practical question this raises is how to verify that data protection measures are effective, rather than relying solely on a general commitment to protect data. Franchisors and franchisees can address this in their discussions as a matter for internal review, not as a new requirement introduced by the Egyptian authorities through the published report.
Practical questions for brand owners and franchisees
As an editorial recommendation, business owners could use this call as a starting point to review some straightforward questions: What customer data does the business hold? Who is authorised to access it? How is responsibility divided between franchisor and franchisee when operating systems are shared? These are questions to examine, not findings the report has made about particular businesses.
When discussing a franchise agreement or reviewing operating arrangements, it may also be useful to request written clarification of responsibilities for handling data and responding to security incidents. This does not mean the source has announced a mandatory contractual template; it is a suggested precaution to avoid leaving responsibilities unclear between the parties.
Practical takeaway: The report concerns a public call for franchise businesses to be required to meet data protection standards, not a confirmed legislative change. For franchisees in Egypt, the practical step is to review responsibilities for protecting customer information and check official sources before treating any reported requirement as a new legal obligation.